Wednesday, November 24, 2010

How to Remove HDD Control (Uninstall Guide)

HDD Control is a fake disk defragmenter and computer optimization program that deliberately reports false information about hard drive, RAM and Windows registry errors. It pretends to run a system check and then reports numerous errors. It states that certain errors are critical and should be fixed immediately. In order to fix the errors you need to run the defragmenter. If you use Windows XP or Windows Vista, HDD Control will make your desktop background black. That won't happen if you use Windows 7. Finally, it will state that some problems and system issues can not be fixes unless you purchase this useless software. Please do not fall victim to this scam. If your computer is infected with this rogue program then please follow the removal instructions below to remove HDD Control from your computer for free using legitimate anti-malware programs.

HDD Control malware is from the same family as Check Disk and Ultra Defragger. Such rogue programs are promoted mostly through the use of trojans, fake online scanners, misleading websites and other malicious software. HDDControl can be also distributed on Facebook, Twitter and other social networks. When the rogue program is running, it will block nearly all programs on your computer and display a fake message with the following text:
Windows detected a hard drive problem.
A hard drive error occurred while starting the application.
However, if you attempt to run a program enough times it will eventually work. HDD Control may hijack your web browser and redirect you to various unrelated websites full of ads or even other malicious software. As a typical scareware, it will display fake alerts and notifications from your Windows taskbar. You may even get a notification that your hard drive is missing. Obviously, that's not true; otherwise your computer wouldn't work at all. The text of some of the alerts you may see include:
Critical Error!
Damaged hard drive clusters detected. Private data is at risk.
Critical Error
Windows can't find hard disk space. Hard drive error
Critical Error
A critical error has occurred while indexing data stored on hard drive. System restart required.
HDD Control's process is a bunch of numbers, e.g. 1648411579.exe. The rogue program keeps the files in Windows Temp folder. Please see the removal instructions below for more information. It goes without saying that HDD Control is a scam. You should contact your credit card provided and dispute the charges if you have already purchased this useless system defragmenter. Then please get rid of HDD Control as soon as possible. Follow the removal instructions below. If you have any questions or additional information about this malware, please leave a comment. Good luck and be safe online!


HDD Control removal instructions using Process Explorer (in Normal mode):

1. Download Process Explorer and end HDD Control process:
  • [SET OF RANDOM CHARACTERS].exe, e.g. 1648411579.exe
2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as Auto Infoistrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


HDD Control removal instructions (in Safe Mode with Networking):

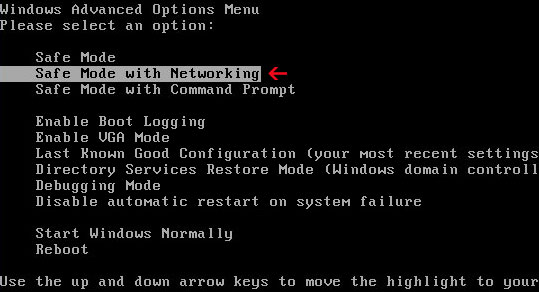
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as Auto Infoistrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


HDD Control associated files and registry values:

Files:
  • %Temp%\[SET OF RANDOM CHARACTERS]
  • %Temp%\[SET OF RANDOM CHARACTERS].exe
  • %Temp%\dfrg
  • %Temp%\dfrgr
  • %Temp%\[SET OF RANDOM CHARACTERS].dll
  • %UserProfile%\Desktop\HDD Control.lnk
  • %UserProfile%\Start Menu\Programs\HDD Control\
  • %UserProfile%\Start Menu\Programs\HDD Control\HDD Control.lnk
  • %UserProfile%\Start Menu\Programs\HDD Control\Uninstall HDD Control.lnk
%Temp% refers to:
C:\Documents and Settings\[UserName]\Local Settings\Temp (in Windows 2000/XP)
C:\Users\[UserName]\AppData\Local\Temp (in Windows Vista & Windows 7)

%UserProfile% refers to:
C:\Documents and Settings\[UserName]\ (in Windows 2000/XP)
C:\Users\[UserName]\ (in Windows Vista & Windows 7)

Registry values:
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS]"
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS].exe"
Share this information with other people:

Tuesday, November 23, 2010

How to remove Check Disk (Uninstall Guide)

Check Disk is a rogue hard drive disk defragmenter and system optimization program that pretends to scan your hard drive disks, registry and system memory for errors. It reports a variety of bogus errors and displays fake messages to scare you into thinking that your computer has some serious problems. Check Disk blocks other programs on your computer and prompts to pay for a full version of the program to remove non-existent computer errors. Do not purchase this rogue program. If your computer is infected with CheckDisk malware then please follow the removal instructions below.

A screen shot of Check Disk


(Thanks to rogueamp)

Check Disk is promoted through the use of trojans and other malicious software, e.g. fake/infected web pages. The authors of the rogue program may also promote it on Facebook, Twitter and other social networks. Once installed, Check Disk will pretend to scan your computer for errors. The scan won't take long. After the fake scan it will report 11 errors and recommend system defragmentation. In Windows XP and Windows Vista it will display fake safe mode screen if you choose to defragment your hard drive. The rogue program won't display the fake safe mode screen if you use Windows 7. That's probably the main difference. Some of the fake computer errors Check Disk detects:
Requested registry access is not allowed. Registry defragmentation required
Read time of hard drive clusters less than 500 ms
Bad sectors on hard drive or damaged file allocation table
Drive C initializing error
Hard drive doesn't respond to system commands
Data Safety Problem. System integrity is at risk.
Registry Error - Critical Error
Furthermore, CheckDisk will block nearly all programs on your computer and display the following error message:
Windows detected a hard drive problem.
A hard drive error occurred while starting the application.

If you attempt to run a program enough times it will eventually work. Last, but least, Check Disk will display fake errors messages and pop ups from your Windows taskbar. The text of some of the alerts you may see include:
Critical Error!
Damaged hard drive clusters detected. Private data is at risk.
Critical Error
Hard Drive not found. Missing hard drive.
Critical Error
RAM memory usage is critically high. RAM memory failure.
System Restore
The system has been restored after a critical error. Data integrity and hard drive integrity verification required.
Check Disk is from the same family as Ultra Defragger and HDD Defragmenter.
Without a doubt, you can not trust this program. It's a scam. You should contact your credit card provider and dispute the charges or even cancel your credit card if you have already purchased Check Disk. Then please follow the removal instructions below to remove Check Disk and related malware from your computer using legitimate anti-malware software. XyliBox and Siri posted the CheckDisk registration code: 0973467457475070215340537432225. We do not guarantee that it will work, just give it a try. Click on Help & Support button and enter the code. If it works, the rogue program won't block malware removal tools and other programs making the removal procedure a bit easier. If you have any questions or additional information about Check Disk, please leave a comment. Good luck and be safe online!


Check Disk removal instructions using Process Explorer (in Normal mode):

1. Download Process Explorer and end Check Disk process:
  • [SET OF RANDOM CHARACTERS].exe
2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as Auto Infoistrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Check Disk removal instructions (in Safe Mode with Networking):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as Auto Infoistrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Check Disk associated files and registry values:

Files:
  • %Temp%\[SET OF RANDOM CHARACTERS]
  • %Temp%\[SET OF RANDOM CHARACTERS].exe
  • %Temp%\dfrg
  • %Temp%\dfrgr
  • %Temp%\[SET OF RANDOM CHARACTERS]>.dll
  • %Temp%\tmp2.tmp
  • %UserProfile%\Desktop\Check Disk.lnk
  • %UserProfile%\Start Menu\Programs\Check Disk\
  • %UserProfile%\Start Menu\Programs\Check Disk\Check Disk.lnk
  • %UserProfile%\Start Menu\Programs\Check Disk\Uninstall Check Disk.lnk
%Temp% refers to:
C:\Documents and Settings\[UserName]\Local Settings\Temp (in Windows 2000/XP)
C:\Users\[UserName]\AppData\Local\Temp (in Windows Vista & Windows 7)

%UserProfile% refers to:
C:\Documents and Settings\[UserName]\ (in Windows 2000/XP)
C:\Users\[UserName]\ (in Windows Vista & Windows 7)

Registry values:
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS]"
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS].exe"
Share this information with other people:

Saturday, November 20, 2010

Privacy Policy

Privacy Policy for computertipsandguide.blogspot.com/ 

If you require any more information or have any questions about our privacy policy, please feel free to contact us by email at salamunalaik22@gmail.com. 

At computertipsandguide.blogspot.com/, the privacy of our visitors is of extreme importance to us. This privacy policy document outlines the types of personal information is received and collected by computertipsandguide.blogspot.com/ and how it is used. 

Log Files
Like many other Web sites, computertipsandguide.blogspot.com/ makes use of log files. The information inside the log files includes internet protocol ( IP ) addresses, type of browser, Internet Service Provider ( ISP ), date/time stamp, referring/exit pages, and number of clicks to analyze trends, administer the site, track user’s movement around the site, and gather demographic information. IP addresses, and other such information are not linked to any information that is personally identifiable. 

Cookies and Web Beacons 
computertipsandguide.blogspot.com/ does use cookies to store information about visitors preferences, record user-specific information on which pages the user access or visit, customize Web page content based on visitors browser type or other information that the visitor sends via their browser. 

DoubleClick DART Cookie 
.:: Google, as a third party vendor, uses cookies to serve ads on computertipsandguide.blogspot.com/.
.:: Google's use of the DART cookie enables it to serve ads to users based on their visit to computertipsandguide.blogspot.com/ and other sites on the Internet. 
.:: Users may opt out of the use of the DART cookie by visiting the Google ad and content network privacy policy at the following URL - http://www.google.com/privacy_ads.html 

Some of our advertising partners may use cookies and web beacons on our site. Our advertising partners include ....
Google Adsense


These third-party ad servers or ad networks use technology to the advertisements and links that appear on computertipsandguide.blogspot.com/ send directly to your browsers. They automatically receive your IP address when this occurs. Other technologies ( such as cookies, JavaScript, or Web Beacons ) may also be used by the third-party ad networks to measure the effectiveness of their advertisements and / or to personalize the advertising content that you see. 

computertipsandguide.blogspot.com/ has no access to or control over these cookies that are used by third-party advertisers. 

You should consult the respective privacy policies of these third-party ad servers for more detailed information on their practices as well as for instructions about how to opt-out of certain practices. computertipsandguide.blogspot.com/'s privacy policy does not apply to, and we cannot control the activities of, such other advertisers or web sites. 

If you wish to disable cookies, you may do so through your individual browser options. More detailed information about cookie management with specific web browsers can be found at the browsers' respective websites.

Friday, November 19, 2010

How to remove Scan Disk (Uninstall Instructions)

Scan Disk is a fake defragmenter and system optimization tool. It is promoted through the use of trojans, fake online scanners and other malicious websites. It can be also distributed via facebook, twitter or other social networks. Basically, Scan Disk will infect your computer to make you think that you have some really serious problems, e.g. hard drive errors, corrupted memory, bad sectors and other stuff. Then this bogus program will try to make you buy its software to fix supposedly found errors and other computer problems. Do not fall victim to Scan Disk because it is nothing more but a rip-off rogue, scam. If you got this annoying program on your computer then please follow the removal instructions below to remove Scan Disk and any other related malware from your computer for free using legitimate anti-malware software.

A screen shot of Scan Disk
ScanDisk is clone of Ultra Defragger, Quick Defragmenter and HDD Defragmenter. As a typical scareware, it will pretend to scan your hard drives and memory for problems. Of course, it will find some critical hard drive and computer memory errors. By the way, it displays the same problems (11 errors) on each infected computer. How rude. Probably the biggest problem is that Scan Disk won't allow you to run other programs on your computer. It will state that this program is corrupted or cannot be found. The fake message reads:
Windows detected a hard drive problem.
A hard drive error occurred while starting the application.


However, if you attempt to run a program enough times it will eventually work. So, don't give up easily. After the fake scan it will display a list of errors:
Drive C initializing error
Bad sectors on hard drive or damaged file allocation table
Read time of hard drive clusters less than 500 ms
Hard drive doesn't respond to system commands
Furthermore, it will display fake alert from your Windows taskbar. Some of the fake alerts that you will see are:
Critical Error!
Damaged hard drive clusters detected. Private data is at risk.
Critical Error
Hard Drive not found. Missing hard drive.
Critical Error
Windows can't find hard disk space. Hard drive error
As you can see, Scan Disk is not a legitimate program. It reports non-existent errors to scare you into purchasing the bogus program. If you have already purchased it then you should contact your credit card provider and dispute the charges or even cancel your credit card. Then please follow the removal instructions below. Please note that Scan Disk and additionally installed malware can download more malicious code onto your computer. Although, you can remove Scan Disk manually, we strongly recommend you to use anti-malware software listed below. And finally, if you have any questions or other information about this malware, please leave a comment. Good luck and be safe online!


Scan Disk removal instructions using Process Explorer (in Normal mode):

1. Download Process Explorer and end Scan Disk process:
  • [SET OF RANDOM CHARACTERS].exe
2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as Auto Infoistrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Scan Disk removal instructions (in Safe Mode with Networking):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as Auto Infoistrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Scan Disk associated files and registry values:

Files:
  • %Temp%\[SET OF RANDOM CHARACTERS]
  • %Temp%\[SET OF RANDOM CHARACTERS].exe
  • %Temp%\dfrg
  • %Temp%\dfrgr
  • %Temp%\[SET OF RANDOM CHARACTERS].dll
  • %Temp%\tmp2.tmp
  • %UserProfile%\Desktop\Scan Disk.lnk
  • %UserProfile%\Start Menu\Programs\Scan Disk\
  • %UserProfile%\Start Menu\Programs\Scan Disk\Scan Disk.lnk
  • %UserProfile%\Start Menu\Programs\Scan Disk\Uninstall Scan Disk.lnk
%Temp% refers to:
C:\Documents and Settings\[UserName]\Local Settings\Temp (in Windows 2000/XP)
C:\Users\[UserName]\AppData\Local\Temp (in Windows Vista & Windows 7)

%UserProfile% refers to:
C:\Documents and Settings\[UserName]\ (in Windows 2000/XP)
C:\Users\[UserName]\ (in Windows Vista & Windows 7)

Registry values:
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS]"
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS].exe"
Share this information with other people:

Monday, November 15, 2010

How to remove Ultra Defragger (Uninstall Guide)

Ultra Defragger is a fake defragmentation tool that deliberately reports fake system and hard drive disk errors to make you think that your computer has some serious problems. Basically, it's a rip-off rogue because it prompts the user to pay for a full version of the program to fix non-existent hard drive and system memory errors. What is more, Ultra Defragger is promoted mostly through the use of infected websites, trojans and other malicious software. The scammers may even distribute it on Facebook and other social networks. If your computer is infected with this rogue program then please follow the removal instructions bellow to remove Ultra Defragger from your computer for free either manually or using legitimate anti-malware software.

A screen shot of Ultra Defragger
UltraDefragger is a very annoying piece of malware from the same family as HDD Defragmenter and Quick Defragmenter. It will hijack your computer, block nearly all programs and display fake error messages. Once installed, it will pretend your hard drives and memory for problems. Then it will display numerous errors (I bet it will find 11 errors) and ask you to pay for a full version of the program to fix the errors. By the way, if you choose to run the defragmentation then it will display a fake Safe Mode background. And when you attempt run a program it will display this error message:
Windows detected a hard drive problem.
A hard drive error occurred while starting the application.


However, it should be noted that if you attempt to run a program enough times it will eventually work. Here are some fake problems that Ultra Defragger detects on a victim's PC:
Requested registry access is not allowed. Registry defragmentation required
Read time of hard drive clusters less than 500 ms
Bad sectors on hard drive or damaged file allocation table
Drive C initializing error
Ram Temperature is 83 C. Optimization is required for normal operation.
Data Safety Problem. System integrity is at risk.
Registry Error - Critical Error
Ultra Defragger will also display fake "ballon messages" from your Windows task bar. Some of the fake alerts read:
Critical Error!
Damaged hard drive clusters detected. Private data is at risk.
Critical Error
Hard Drive not found. Missing hard drive.
Critical Error
RAM memory usage is critically high. RAM memory failure.

Critical Error
Windows can't find hard disk space. Hard drive error
As you can see, Ultra Defragger will claim that your hard drive is missing. That's actually impossible because otherwise you won't be able to use your computer at all. Without a doubt, UltraDefragger is nothing more but a scam. If you have already purchased it then you hould contact your credit card provider and dispute the charges and even cancel your credit card. Then please follow the removal instructions bellow. And finally, you should definitely scan your computer with at least two anti-malware programs, e.g. Malwarebytes' AntiMalware and Hitman pro ta make sure that you are not a part of a botnet and that Ultra Defragger and related malware were successfully removed from your computer. If you have any questions or additional information about Ultra Defragger, please leave a comment. Good luck and be safe!


Ultra Defragger removal instructions using Process Explorer (in Normal mode):

1. Download Process Explorer and end Ultra Defragmenter process:
  • [SET OF RANDOM CHARACTERS].exe
2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as Auto Infoistrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Ultra Defragger removal instructions (in Safe Mode with Networking):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as Auto Infoistrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Ultra Defragger associated files and registry values:

Files:
  • %Temp%\[SET OF RANDOM CHARACTERS]
  • %Temp%\[SET OF RANDOM CHARACTERS].exe
  • %Temp%\dfrg
  • %Temp%\dfrgr
  • %Temp%\[SET OF RANDOM CHARACTERS]>.dll
  • %Temp%\tmp2.tmp
  • %UserProfile%\Desktop\Ultra Defragger.lnk
  • %UserProfile%\Start Menu\Programs\Ultra Defragger\
  • %UserProfile%\Start Menu\Programs\Ultra Defragger\Ultra Defragger.lnk
  • %UserProfile%\Start Menu\Programs\Ultra Defragger\Uninstall Ultra Defragger.lnk
%Temp% refers to:
C:\Documents and Settings\[UserName]\Local Settings\Temp (in Windows 2000/XP)
C:\Users\[UserName]\AppData\Local\Temp (in Windows Vista & Windows 7)

%UserProfile% refers to:
C:\Documents and Settings\[UserName]\ (in Windows 2000/XP)
C:\Users\[UserName]\ (in Windows Vista & Windows 7)

Registry values:
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS]"
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS].exe"
Share this information with other people:

Saturday, November 13, 2010

Remove Vista Antispyware 2011 and Vista Security 2011 (Uninstall Guide)

Vista Antispyware 2011, Vista Security 2011 and Vista Antimalware 2011 are a few names of the same rogue security program that intentionally misrepresents the security status of your computer, pretends to scan your computer for malicious software and blocks certain executable files (.exe) from running. The scam is intended to frighten you into purchasing the fake program. Please do not purchase Vista Antispyware 2011, Vista Antimalware 2011 or any other rogue program from the list below. This rogue program is downloaded mostly by trojans that come from fake online scanners, infected websites or spam emails. The bad guys may also distribute their bogus products on Facebook, Twitter and other social networks. If you got hit by this rogue security program please follow the removal instructions below.

This rogue program goes by many different program names listed below.
  • Vista Antispyware
  • Vista Antispyware 2011
  • Vista Anti-Virus 
  • Vista Anti-Virus 2011
  • Vista Home Security
  • Vista Home Security 2011
  • Vista Security
  • Vista Security 2011
  • Vista Internet Security
  • Vista Internet Security 2011
  • Vista Antimalware
  • Vista Antimalware 2011
  • Vista Guard
  • Vista Total Security
  • Vista Total Security 2011
A screen shot of Vista Security 2011
Vista Antispyware 2011, Vista Security 2011 or Vista Antimalware 2011 pretends to be a security update for Windows. The fake Windows update looks quite convincing. Once the rogue program is installed, it will inform you that you are infected with new threats. The misleading application will then present itself and run a scan of the system. Of course, it will find numerous infections on your computer and then will ask you to pay for a full version of the program. Furthermore, the rogue program will block legitimate anti-malware software. The main process of this rogue program pw.exe and several newly added Windows registry values will launch the rogue program instead of the requested executable, e.g. Task Manager or MS Paint. While Vista Antispyware 2011 or Vista Guard is running, it will display numerous security alerts and "balloon messages" that appear in the lower right-hand side of the system. The rogue program will claim that Internet Explorer is infected with keylogger or that private data can be stolen by third parties. Some of the fake alerts read:
Vista Antispyware 2011 Firewall Alert
Vista Antispyware 2011 has blocked a program from accessing the internet
Internet Explorer is infected with Trojan-BNK.Win32.Keylogger.gen
Private data can be stolen by third parties, including credit card details and passwords.
Privacy threat!
Spyware intrusion detected. Your system is infected. System integrity is at risk. Private data can be stolen by third parties, including credit card details and passwords. Click here to perform a security repair.
The scan results and security warnings produced by the misleading application are entirely false and should be ignored. Last, but not least, this fake program will hijack Internet Explorer and Mozilla Firefox. It will display a fake alert message and block nearly all websites you attempt to visit. The message that you will see is:
Internet Explorer alert. Visiting this site may pose a security threat to your system!
Possible reasons include:
- Dangerous code found in this site's pages which installed unwanted software into your system.
- Suspicious and potentially unsafe network activity detected.
- Spyware infections in your system
- Complaints from other users about this site.
- Port and system scans performed by the site being visited.


Things you can do:
- Get a copy of Vista Antispyware 2011 to safeguard your PC while surfing the web (RECOMMENDED)
- Run a spyware, virus and malware scan
- Continue surfing without any security measures (DANGEROUS)


It goes without saying that you should remove this rogue program from your computer as soon as possible. It exaggerates the problems on the system and refuse to fix them until the vendor is paid. Please do not pay for a program that doesn't work. It will give you a false sense of security and may eve leads to potentially greater risks from more aggressive threats. If you have already purchased this bogus program then you should contact your credit card company and dispute the charges. We also recommend you to cancel your credit card. Finally, please follow the removal instructions below to remove Vista Antispyware 2011, Vista Security 2011 or Vista Antimalware 2011 from your computer for free using legitimate anti-malware applications. If you have any questions or additional information about this malware, please leave a comment. Good luck and be safe online!


Vista Antispyware 2011, Vista Security 2011 or Vista Antimalware 2011 removal instructions:

1. Click Start->Run or press WinKey+R. Type in "command" and press Enter key.


2. In the command prompt window type "notepad" and press Enter key. Notepad will come up.


3. Copy all the text in blue color below and paste to Notepad.

Windows Registry Editor Version 5.00

[-HKEY_CURRENT_USER\Software\Classes\.exe\shell\open\command]
[-HKEY_CURRENT_USER\Software\Classes\secfile\shell\open\command]
[-HKEY_CLASSES_ROOT\.exe\shell\open\command]
[HKEY_CLASSES_ROOT\.exe]
@="exefile"
"Content Type"="application/x-msdownload"

[-HKEY_CLASSES_ROOT\secfile]

4. Save file as fix.reg to your Desktop. NOTE: (Save as type: All files)


5. Double-click on the fix.reg file to run it. Click "Yes" for Registry Editor prompt window. Then click OK.
6. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as Auto Infoistrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

7. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET NOD32 Antivirus 4.


Associated Vista Antispyware 2011, Vista Security 2011 or Vista Antimalware 2011 files and registry values:

Files:
  • C:\ProgramData\[SET OF RANDOM CHARACTERS]
  • C:\Users\AppData\Local\[3 RANDOM CHARACTERS].exe
  • C:\Users\AppData\Local\[SET OF RANDOM CHARACTERS]
  • C:\Users\AppData\Roaming\Microsoft\Windows\Templates\[SET OF RANDOM CHARACTERS]
  • C:\Users\[Username]\AppData\Local\Temp\[SET OF RANDOM CHARACTERS]
For example:
[SET OF RANDOM CHARACTERS] = d6e3porotq7359g8rm1q286zx
[3 RANDOM CHARACTERS].exe = hyf.exe

Registry values:
  • HKEY_CURRENT_USER\Software\Classes\.exe "(Default)" = 'exefile'
  • HKEY_CURRENT_USER\Software\Classes\.exe "Content Type" = 'application/x-msdownload'
  • HKEY_CURRENT_USER\Software\Classes\.exe\DefaultIcon "(Default)" = '%1' = '"C:\Users\AppData\Local\[3 RANDOM CHARACTERS].exe.exe" /START "%1" %*'
  • HKEY_CURRENT_USER\Software\Classes\.exe\shell\open\command "IsolatedCommand" = '"%1" %*'
  • HKEY_CURRENT_USER\Software\Classes\.exe\shell\runas\command "(Default)" = '"%1" %*'
  • HKEY_CURRENT_USER\Software\Classes\.exe\shell\runas\command "IsolatedCommand" = '"%1" %*'
  • HKEY_CURRENT_USER\Software\Classes\exefile "(Default)" = 'Application'
  • HKEY_CURRENT_USER\Software\Classes\exefile "Content Type" = 'application/x-msdownload'
  • HKEY_CURRENT_USER\Software\Classes\exefile\DefaultIcon "(Default)" = '%1'
  • HKEY_CURRENT_USER\Software\Classes\exefile\shell\open\command "(Default)" = '"C:\Users\AppData\Local\[3 RANDOM CHARACTERS].exe" /START "%1" %*'
  • HKEY_CURRENT_USER\Software\Classes\exefile\shell\open\command "IsolatedCommand" = '"%1" %*'
  • HKEY_CURRENT_USER\Software\Classes\exefile\shell\runas\command "(Default)" = '"%1" %*'
  • HKEY_CURRENT_USER\Software\Classes\exefile\shell\runas\command "IsolatedCommand" - '"%1" %*'
  • HKEY_CLASSES_ROOT\.exe\DefaultIcon "(Default)" = '%1'
  • HKEY_CLASSES_ROOT\.exe\shell\open\command "(Default)" = '"C:\Users\AppData\Local\[3 RANDOM CHARACTERS].exe" /START "%1" %*'
  • HKEY_CLASSES_ROOT\.exe\shell\open\command "IsolatedCommand" = '"%1" %*'
  • HKEY_CLASSES_ROOT\.exe\shell\runas\command "(Default)" = '"%1" %*'
  • HKEY_CLASSES_ROOT\.exe\shell\runas\command "IsolatedCommand" = '"%1" %*'
  • HKEY_CLASSES_ROOT\exefile "Content Type" = 'application/x-msdownload'
  • HKEY_CLASSES_ROOT\exefile\shell\open\command "IsolatedCommand" = '"%1" %*'
  • HKEY_CLASSES_ROOT\exefile\shell\runas\command "IsolatedCommand" = '"%1" %*'
  • HKEY_CLASSES_ROOT\exefile\shell\open\command "(Default)" = '"C:\Users\AppData\Local\[3 RANDOM CHARACTERS].exe" /START "%1" %*'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\open\command "(Default)" = '"C:\Users\AppData\Local\[3 RANDOM CHARACTERS].exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe"'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\safemode\command "(Default)" = '"C:\Users\AppData\Local\[3 RANDOM CHARACTERS].exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe" -safe-mode'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\IEXPLORE.EXE\shell\open\command "(Default)" = '"C:\Users\AppData\Local\[3 RANDOM CHARACTERS].exe" /START "C:\Program Files\Internet Explorer\iexplore.exe"'
Share this information with other people:

Remove XP Antispyware 2011 and XP Guard (Uninstall Guide)

XP Antispyware 2011, XP Guard or XP Internet Security 2011 are only a few names of the same fake security program. Basically, it's a name changing rip-off rogue application that deliberately reports false system security threats. Some other names of this misleading program are listed below. This fake program (XP Antispyware 2011, XP Guard or any other name from the list) is quite aggressive. It comes from fake online scanners, infected websites or bundled with other malware and masquerades as the security update for Windows. The rogue program drops an executable on the computer which blocks legitimate anti-virus and anti-spyware programs and causes some other problems. XP Internet Security 2011 or XP Antimalware 2011 also modifies Windows registry and makes the removal process even more complicated. Thankfully, we've got the remove instructions to help you to remove XP Antispyware 2011, XP Guard or XP Internet Security 2011 from your computer. Please follow the instructions below carefully.

This rogue program goes by many different program names listed below.
  • XP Antispyware
  • XP Antispyware 2011
  • XP Anti-Virus
  • XP Anti-Virus 2011
  • XP Total Security
  • XP Total Security 2011
  • XP Security
  • XP Security 2011
  • XP Internet Security
  • XP Internet Security 2011
  • XP Antimalware
  • XP Antimalware 2011
  • XP Guard
  • XP Home Security 2011


While XP Antispyware 2011 is running, it will pretend to scan your computer for malicious code. Obviously, it will find numerous infections, e.g. e-mail worms, trojans, spyware and other malicious software on your computer. Then it will ask you to pay for a full version of the program to remove the infections which do not even exist. Please do not fall victim to this scam. As a typical rogue, XP Antispyware 2011, XP Security or any other other name, will display fake security warnings and notification from your Windows taskbar. The text of some of the fake alerts is:
System danger!
Your system security is in danger. Privacy threats detected. Spyware, keyloggers or Trojans may be working the background right now. Perform an in-depth scan and removal now, click here.
Stealth intrusion!
Infection detected in the background. Your computer is now attacked by spyware and rogue software. Eliminate the infection safely, perform a security scan and deletion now.

Privacy threat!
Spyware intrusion detected. Your system is infected. System integrity is at risk. Private data can be stolen by third parties, including credit card details and passwords. Click here to perform a security repair.


So, as you can see, the rogue program does all its best to scare you into thinking that your computer is infected with spyware, trojans and other viruses. It will even claim that your sensitive information will be stolen and sold. Don't worry, all these alerts are fake. You just need to remove the rogue program and maybe some related malware from your computer and you will be good to go. XP Antispyware 2011 or XP Guard will also hijack Intenet Explorer and Mozilla Firefox. The problem is that you won't be able to download malware removal software. The rogue program will display a fake alert that the site you are visiting is dangerous. Of course, that’s not true. The fake message reads:
Internet Explorer alert. Visiting this site may pose a security threat to your system!
Possible reasons include:
- Dangerous code found in this site's pages which installed unwanted software into your system.
- Suspicious and potentially unsafe network activity detected.
- Spyware infections in your system
- Complaints from other users about this site.
- Port and system scans performed by the site being visited.


Things you can do:
- Get a copy of XP Antispyware 2011 to safeguard your PC while surfing the web (RECOMMENDED)
- Run a spyware, virus and malware scan
- Continue surfing without any security measures (DANGEROUS)


Last, but not least, XP Antispyware 2011 will block certain programs on your computer. So, first of all you will have to stop the rogue program and fix the registry. If your PC is heavily you will need to use a different computer than the infected one to download and transfer all the necessary files required to remove the rogue program. By the way, if you have already purchased this bogus program then you should contact your credit card company and dispute the charges or even cancel your credit card. Then please follow the removal instructions below. If you have any questions or additional information about XP Antispyware 2011, XP Guard or XP Internet Security 2011, please leave a comment. Good luck and be safe online!


XP Antispyware 2011, XP Guard, XP Internet Security 2011 removal instructions:

1. Click Start->Run or press WinKey+R. Type in "command" and press Enter key.


2. In the command prompt window type "notepad" and press Enter key. Notepad will come up.


3. Copy all the text in blue color below and paste to Notepad.

Windows Registry Editor Version 5.00

[-HKEY_CURRENT_USER\Software\Classes\.exe]
[-HKEY_CURRENT_USER\Software\Classes\secfile]
[-HKEY_CLASSES_ROOT\secfile]
[-HKEY_CLASSES_ROOT\.exe\shell\open\command]

[HKEY_CLASSES_ROOT\exefile\shell\open\command]
@="\"%1\" %*"

[HKEY_CLASSES_ROOT\.exe]
@="exefile"
"Content Type"="application/x-msdownload"

4. Save file as fix.reg to your Desktop. NOTE: (Save as type: All files)


5. Double-click on fix.reg file to run it. Click "Yes" for Registry Editor prompt window. Then click OK.
6. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as Auto Infoistrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

7. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET NOD32 Antivirus 4.


Alternate removal instructions:

Make sure that you can see hidden and operating system protected files in Windows. For more in formation, please read Show Hidden Files and Folders in Windows.

Under the Hidden files and folders section, click Show hidden files and folders, and remove the checkmarks from the checkboxes labeled:
  • Hide extensions for know file types
  • Hide protected operating system files
Click OK to save the changes.


1. Go into C:\Documents and Settings\[UserName]\Local Settings\Application Data\ folder.

For example: C:\Documents and Settings\Michael\Local Settings\Application Data\


2. Find hidden executable file in this folder. In our case it was called wmi.exe, but I'm sure that the file name will be different in your case. Rename wmi.exe to wmi.dl_ and click Yes to confirm file rename. Then restart your computer.


3. After a restart, open Internet Explorer. Download xp_exe_fix.reg and save it to your Desktop. Double-click on xp_exe_fix.reg to run it. Click "Yes" for Registry Editor prompt window. Click OK.


4. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as Auto Infoistrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

5. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET NOD32 Antivirus 4.


Associated XP Antispyware 2011, XP Guard, XP Internet Security 2011 files and registry values:

Files:
  • C:\Documents and Settings\All Users\[SET OF RANDOM CHARACTERS]
  • C:\Documents and Settings\[UserName]\Application Data\[SET OF RANDOM CHARACTERS]
  • C:\Documents and Settings\[UserName]\Local Settings\Application Data\[3 RANDOM CHARACTERS].exe
  • C:\Documents and Settings\[UserName]\Templates\[SET OF RANDOM CHARACTERS]
  • C:\Documents And Settings\[UserName]\Local Settings\Temp\[SET OF RANDOM CHARACTERS]
For example: [SET OF RANDOM CHARACTERS] = d5a8krfpei0913mt2ts3px3c78qw

Registry values:
  • HKEY_CURRENT_USER\Software\Classes\.exe "(Default)" = 'exefile'
  • HKEY_CURRENT_USER\Software\Classes\.exe "Content Type" = 'application/x-msdownload'
  • HKEY_CURRENT_USER\Software\Classes\.exe\DefaultIcon "(Default)" = '%1' = '"C:\Documents and Settings\[UserName]\Local Settings\Application Data\[3 RANDOM CHARACTERS].exe" /START "%1" %*'
  • HKEY_CURRENT_USER\Software\Classes\.exe\shell\open\command "IsolatedCommand" = '"%1" %*'
  • HKEY_CURRENT_USER\Software\Classes\.exe\shell\runas\command "(Default)" = '"%1" %*'
  • HKEY_CURRENT_USER\Software\Classes\.exe\shell\runas\command "IsolatedCommand" = '"%1" %*'
  • HKEY_CURRENT_USER\Software\Classes\exefile "(Default)" = 'Application'
  • HKEY_CURRENT_USER\Software\Classes\exefile "Content Type" = 'application/x-msdownload'
  • HKEY_CURRENT_USER\Software\Classes\exefile\DefaultIcon "(Default)" = '%1'
  • HKEY_CURRENT_USER\Software\Classes\exefile\shell\open\command "(Default)" = '"C:\Documents and Settings\[UserName]\Local Settings\Application Data\[3 RANDOM CHARACTERS].exe" /START "%1" %*'
  • HKEY_CURRENT_USER\Software\Classes\exefile\shell\open\command "IsolatedCommand" = '"%1" %*'
  • HKEY_CURRENT_USER\Software\Classes\exefile\shell\runas\command "(Default)" = '"%1" %*'
  • HKEY_CURRENT_USER\Software\Classes\exefile\shell\runas\command "IsolatedCommand" - '"%1" %*'
  • HKEY_CLASSES_ROOT\.exe\DefaultIcon "(Default)" = '%1'
  • HKEY_CLASSES_ROOT\.exe\shell\open\command "(Default)" = '"C:\Documents and Settings\[UserName]\Local Settings\Application Data\[3 RANDOM CHARACTERS].exe" /START "%1" %*'
  • HKEY_CLASSES_ROOT\.exe\shell\open\command "IsolatedCommand" = '"%1" %*'
  • HKEY_CLASSES_ROOT\.exe\shell\runas\command "(Default)" = '"%1" %*'
  • HKEY_CLASSES_ROOT\.exe\shell\runas\command "IsolatedCommand" = '"%1" %*'
  • HKEY_CLASSES_ROOT\exefile "Content Type" = 'application/x-msdownload'
  • HKEY_CLASSES_ROOT\exefile\shell\open\command "IsolatedCommand" = '"%1" %*'
  • HKEY_CLASSES_ROOT\exefile\shell\runas\command "IsolatedCommand" = '"%1" %*'
  • HKEY_CLASSES_ROOT\exefile\shell\open\command "(Default)" = '"C:\Documents and Settings\[UserName]\Local Settings\Application Data\[3 RANDOM CHARACTERS].exe" /START "%1" %*'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\open\command "(Default)" = '"C:\Documents and Settings\[UserName]\Local Settings\Application Data\[3 RANDOM CHARACTERS].exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe"'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\safemode\command "(Default)" = '"C:\Documents and Settings\[UserName]\Local Settings\Application Data\[3 RANDOM CHARACTERS].exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe" -safe-mode'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\IEXPLORE.EXE\shell\open\command "(Default)" = '"C:\Documents and Settings\[UserName]\Local Settings\Application Data\[3 RANDOM CHARACTERS].exe" /START "C:\Program Files\Internet Explorer\iexplore.exe"'
Share this information with other people: