Tuesday, November 1, 2011

Remove Adjectivesearchsystem.com (Uninstall Guide)

Adjectivesearchsystem.com is a ZeroAccess/Sirefef rootkit-related browser hijacker that redirects users to totally different web pages having nothing to do with the search inquiries while searching with Google, Bing and other search engines. While the redirect is loading it says Waiting for adjectivesearchsystem.com and then goes straight to spam websites or even worse, sites that load malicious software.


Not only is this annoying and frustrating, but it can potentially be very harmful to your computer if you don't do anything about it. As a matter of fact, sometimes ZeroAccess rootkit drops a virus called Virus.Win32.RLoader.a. That's how Kaspersky identifies it. Besides, ZeroAccess/Sirefef alone is a very frustrating rootkit, it injects Windows system files to bypass Firewalls. It goes without saying that you need to delete this virus from your computer.

Users usually have no idea how they've gotten this virus on their PCs. However, it's very easy to identify this virus because it starts a process with a very unique name with the following structure: numbers:numbers.exe, for example 2324325:6823764.exe.


Unfortunately, you can end it and you can't delete the malicious files manually. The infected file has to be repaired. Thankfully, there tools designed to remove ZeroAccess/Sirefef and associated malware: Webroot ZeroAccess removal tool and TDSSKiller. Both utilities are free. Then you should use recommend anti-malware software to remove the leftovers or additionally installed malware from your computer. To remove the rootkit and to stop adjectivesearchsystem.com redirects, please follow the removal instructions below. If you need help removing this virus, please leave a comment below. Good luck and be safe online!


Adjectivesearchsystem.com removal instructions:

1. First of all, download and run ZeroAccess/Sirefef/MAX++ removal tool. (works on 32-bit systems only!)

2. Then use TDSSKiller.

3. Finally, scan your computer with recommend anti-malware software (STOPzilla) to remove the leftovers of this virus from your computer.

It's possible that an infection is blocking STOPzilla from properly installing. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe. Don't forget to update the installed program before scanning.

Alternate malware removal tools can be used in case STOPzilla has missed a threat:
NOTE: if you get the following Windows Security Alert, please click on Unblock button. This alert is caused by ZeroAccess rootkit.


Share this information with your friends:

Saturday, October 29, 2011

Remove Rattlingsearchsystem.com (Uninstall Guide)

Rattlingsearchsystem.com is a ZeroAccess/Sirefef rootkit-related browser hijacker that redirects users to shady websites while searching on Google and other web search engines. It may occasionally open new tabs in your web browser advertising certain websites or services, for example WeLoveFilms community toolbar. The ZeroAccess is probably one of the most nastiest infections circulating on the Internet. Although, the are numerous 'symptoms' that may help you to determine whether or not your computer is infected with this rootkit, the most widely known and discussed is the web browser redirect or every often just Google redirect virus. Whenever you click on any of the search results, the status bar at the bottom of the web browser says Waiting for rattlingsearchsystem.com.


What does it mean? To put it simply, ZeroAccess/Sirefef rootkit injects legitimate Windows system files and configures your computer to redirect web browser request through web servers controlled by cyber criminals. Profit is the main motivation for them, so they may display various ads and redirect you to spam websites to to earn quick cash. What is more, Windows Firewall alerts may show up occasionally asking you to unblock certain applications. It blocks legitimate security products as well. And last, but not least, Rattlingsearchsystem.com infection has a very unique structure that sets this virus apart from malware. Just open up Task Manager and you'll see an active process named 3483441318:42842844.exe or something like that.


That's a very clear sing of ZeroAccess/Sirefef infection. So, to stop rattlingsearchsystem.com redirects and to remove the rootkit from your computer, please follow the removal instructions below. If you need help removing this virus, please leave a comment below. Good luck and be safe online!


Rattlingsearchsystem.com removal instructions:

1. First of all, download and run ZeroAccess/Sirefef/MAX++ removal tool. (works on 32-bit systems only!)

2. Then use TDSSKiller.

3. Finally, scan your computer with recommend anti-malware software (STOPzilla) to remove the leftovers of this virus from your computer.

It's possible that an infection is blocking STOPzilla from properly installing. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe. Don't forget to update the installed program before scanning.

Alternate malware removal tools can be used in case STOPzilla has missed a threat:
NOTE: if you get the following Windows Security Alert, please click on Unblock button. This alert is caused by ZeroAccess rootkit.


Share this information with your friends:

Thursday, October 27, 2011

Remove Signalsearchsystem.com (Uninstall Guide)

Signalsearchsystem.com is a ZeroAccess rootkit-related browser hijacker that redirects users to malicious and very often completely irrelevant web pages. Web search engines, let's say Google or Yahoo!, generate a normal list of search results. If you click on any of the results however, the status bar at the bottom of the web browser says Waiting for signalsearchsystem.com.


What this rootkit actually does is route you to the fake search engine and then redirect to malicious web page or websites filled with advertisements. If the keyword is not profitable ZeroAccess related malware will simply load the requested website. One way or another, you will notice that websites are taking longer to load than usual. Not to mention that random pop-up ads may appear on your computer screen advertising products and services, for example WeLoveFilms toolbar.

What is more, Windows Firewall alerts may show up occasionally asking you to unblock certain applications. That's because ZeroAccess rootkit injects malicious code into system files to bypass Windows firewall.


But probably the most common sign of this infection is a randomly named process running on your computer. It has a very specific structure, there's no way you won't recognize it: numbers:numbers.exe, for example 516841384:54383211.exe.


The bad news is, that you can't end it manually. Doing sustem restore won't help either. ZeroAccess rootkit injects malicious code into Windows system files. You can't just delete them, you need to repair those files otherwise your machine may become unresponsive. The good news however, is that you can use Webroot's ZeroAccess removal tool and TDSSKiller to remove the rootkit. Both tools are free and safe. So, to stop signalsearchsystem.com redirects and to remove the rootkit from your computer, please follow the removal instructions below. Please note, that your should scan your computer with recommend anti-malware software to remove the leftovers of this infection and additionally downloaded malware. If you need help removing this virus, please leave a comment below. Good luck and be safe online!

http://computertipsandguide.blogspot.com


Signalsearchsystem.com removal instructions:

1. First of all, download and run ZeroAccess/Sirefef/MAX++ removal tool. (works on 32-bit systems only!)

2. Then use TDSSKiller.

3. Finally, scan your computer with recommend anti-malware software (STOPzilla) to remove the leftovers of this virus from your computer.

It's possible that an infection is blocking STOPzilla from properly installing. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe. Don't forget to update the installed program before scanning.

Alternate malware removal tools can be used in case STOPzilla has missed a threat:
NOTE: if you get the following Windows Security Alert, please click on Unblock button. This alert is caused by ZeroAccess rootkit.


Share this information with your friends:

Wednesday, October 26, 2011

Colossalsearchsystem.com (Uninstall Guide)

Colossalsearchsystem.com is a ZeroAccess/Serifef-related browser hijacker that will take you to malicious and adware websites instead of the one you wanted. Although, the address in the URL box of your web browser shows the correct web address, the actual web page displayed is completely different and very often irrelevant to what you were searching for. This very annoying and sophisticated rootkit blocks certain system tools and legitimate antivirus programs. It says "Windows cannot access the specified device, path, or file. You may not have the appropriate permissions to access the item."

At the bottom of your web browser you'll see that it's accesing colossalsearchsystem.com instead of the intended website. It's a fake search engine and browser hijacker at the same time. You will notice that search results take longer to appear, however, if you type in the website manually it works fine.


Windows Firewall alerts may show up from time to time asking you to unblock certain applications. That's because ZeroAccess rootkit injects malicious code into system files to bypass Windows firewall.


And probably the most clear sign of this infection is a questionable process named numbers:numbers, for example 238466872:32468238.exe.


This process is protected, you can't just terminate it as any other system process. Doing system restore won't help either. First of all, you need to remove the rootkit; otherwise you won't be able to run anti-malware software. Thankfully, there are a couple of tools designed to remove ZeroAccess rootkit from the system. To remove the rootkit and to stop colossalsearchsystem.com redirects, please follow the removal instructions below. Good luck and be safe online!

http://computertipsandguide.blogspot.com


Colossalsearchsystem.com removal instructions:

1. First of all, download and run ZeroAccess/Sirefef/MAX++ removal tool. (works on 32-bit systems only!)

2. Then use TDSSKiller.

3. Finally, scan your computer with recommend anti-malware software (STOPzilla) to remove the leftovers of this virus from your computer.

It's possible that an infection is blocking STOPzilla from properly installing. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe. Don't forget to update the installed program before scanning.

Alternate malware removal tools can be used in case STOPzilla has missed a threat:
NOTE: if you get the following Windows Security Alert, please click on Unblock button. This alert is caused by ZeroAccess rootkit.


Share this information with your friends:

Tuesday, October 25, 2011

Remove Raresearchsystem.com (Uninstall Guide)

Raresearchsystem.com is a ZeroAccess/Serifef-related browser hijacker. It redirects users to spam and malicious websites, displays bogus advertisements and blocks legitimate antivirus products. The most common symptoms of this infection:
  • can't run/install antivirus software
  • anti-malware programs crash mid-scan
  • browser redirects
  • annoying pop-up advertisements
  • slowed computer performance
  • slow internet connection speed
You may also notice that Windows firewall turns off automatically. ZeroAccess rootkit injects malcode into legit Windows processes to avoid detection and bypass Windows firewall. It displays the correct location/URL in the address bar but loads entirely different website. Waiting for raresearchsystem.com at the bottom of your web browser is another clear sign of this infection.


Fire up Task Manager and you'll quickly notice a questionable process named numbers:numbers, for example 635210245:4362882.exe. You can't terminate it manually. If you attempt to open up the properties for this offending process, you'll the message that windows can't find the location of this executable file. Doing system restore might help, but just for a while. The virus and raresearchsystem.com redirects returns, even though you've done a system restore. This is rather sophisticated malware. Thankfully, there are tools that can handle this virus. Webroot's ZeroAccess removal tool and TDSSKiller by Kaspersky. The first one works only on 32-bit system. To stop raresearchsystem.com redirects and remove ZeroAccess/Serifef rootkit from your computer, please follow the steps in the removal guide below. If you have any questions, please leave a comment. Good luck and be safe online!

http://computertipsandguide.blogspot.com


Raresearchsystem.com removal instructions:

1. First of all, download and run ZeroAccess/Sirefef/MAX++ removal tool. (works on 32-bit systems only!)

2. Then use TDSSKiller.

3. Finally, scan your computer with recommend anti-malware software (STOPzilla) to remove the leftovers of this virus from your computer.

It's possible that an infection is blocking STOPzilla from properly installing. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe. Don't forget to update the installed program before scanning.

Alternate malware removal tools can be used in case STOPzilla has missed a threat:
NOTE: if you get the following Windows Security Alert, please click on Unblock button. This alert is caused by ZeroAccess rootkit.


Share this information with your friends:

Monday, October 24, 2011

Remove Uncommonsearchsystem.com (Uninstall Guide)

Uncommonsearchsystem.com is a ZeroAccess/Serifef-related browser hijacker that redirects users to spam and malicious websites. This rootkit injects malcode into legit Windows processes in order to bypass firewall detection. Usually, this sophisticated malware injects lsass.exe, nevertheless it may inject any other legit Windows process as well. ZeroAccess may randomly redirect you to uncommonsearchsystem.com and other websites full of advertisements and malware. It displays the correct location/URL in the address bar but loads entirely different website. Websites may take longer to load. In some cases this virus displays blank page instead of requested website.


If you're using Google Chrome, ZeroAccess may show an ad promoting WeLoveFilms community toolbar. This toolbar works with other web browsers too, but for some reason I've got this advertisement only in Google Chrome. Another very clear sign of uncommonsearchsystem.com infection is and active process that has the following structure: numbers:numbers.exe, for example 14336673:87263482.exe. To stop annoying redirects, you need to remove the rootkit. There's no other way. The bad news is that you can't remove it manually. What is more, ZeroAccess rootkit blocks legitimate anti-virus and anti-malware programs. Thankfully, you can disinfect your computer using two great utilities: TDSSKiller and ZeroAccess removal tool. Both are free and disables the rootkit. However, the second one works only on 32-bit systems. If you have a 64-bit system, please run only TDSSKiller. Then scan your computer with recommend malware removal tool to remove the leftovers of this virus and to stop uncommonsearchsystem.com. For more information, please follow the removal instructions below. If you have any questions, please leave a comment below. Good luck and be safe online!

http://computertipsandguide.blogspot.com


Uncommonsearchsystem.com removal instructions:

1. First of all, download and run ZeroAccess/Sirefef/MAX++ removal tool. (works on 32-bit systems only!)

2. Then use TDSSKiller.

3. Finally, scan your computer with recommend anti-malware software (STOPzilla) to remove the leftovers of this virus from your computer.

It's possible that an infection is blocking STOPzilla from properly installing. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe. Don't forget to update the installed program before scanning.

Alternate malware removal tools can be used in case STOPzilla has missed a threat:
NOTE: if you get the following Windows Security Alert, please click on Unblock button. This alert is caused by ZeroAccess rootkit.


Share this information with your friends:

Sunday, October 23, 2011

How to Remove System Security 2011 (Uninstall Guide)

System Security 2011 is scareware (a form of scam) that tries to frighten you into purchasing worthless anti-virus product. Don't be fooled! It poses as a legitimate security product, displays a bunch of bogus security alerts, and claims that it's necessary to remove critical malware infections from your computer (which do not even exist). To identify fake antivirus product is pretty simple, however, if that's the first time you've got infected by fake AV you may not recognize this scam right away. Online promotions for fake antivirus products has decreased recently, however, System Security 2011and similar scareware still proliferate across the Internet. So, what should you do if your computer got infected with this malware? First of all, take a deep breath and remain calm. Fake AVs are not so dangerous but very annoying. They can't delete your files, monitor financial transactions, steal Facebook password, etc.

The motivation for malware creators is profit. Do not pay for System Security 2011. If you've already bought it, please contact your credit card company and dispute the charges. You should also consider closing your current credit card and creating a new one. Cyber crooks may sell your credit card information on the underground forums. And finally, please follow the removal instructions below to remove System Security 2011 and associated malware from your computer. It's worth mentioning that System Security 2011 may come bundled with a rootkit. Rootkit is a are very sophisticated malware and may block legitimate anti-malware products. It is wise to run a rootkit removal tool before using anti-malware or anti-virus scanner. Hopefully, I made it a bit clear. Now, as you know what's going on, please follow the steps in the removal guide below very carefully. Especially the alternate manual removal guide, if you choose to remove this virus manually. Last, but not least, if you need any help, please leave a comment below. Good luck and be safe online!

Here's what the rogue antivirus called System Security 2011 looks like. Unique design, looks like an iPad to me :)


A couple of fake security alerts you may see when this rogue antivirus is active.


By far the most easiest way to get rid of System Security 2011 is to use the debugged activation code 9992665263 and run anti-malware software.

http://computertipsandguide.blogspot.com


System Security 2011 removal instructions:

1. First of all, download and run ZeroAccess/Sirefef/MAX++ removal tool. (works on 32-bit systems only!)

2. Then use TDSSKiller.

3. And finally, download recommended anti-malware software (STOPzilla) to remove this virus from your computer.

NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as Auto Infoistrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

If you can't download it, please reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Open Internet Explorer and download STOPzilla. Once finished, go back into Normal Mode and run it. That's It!

Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm
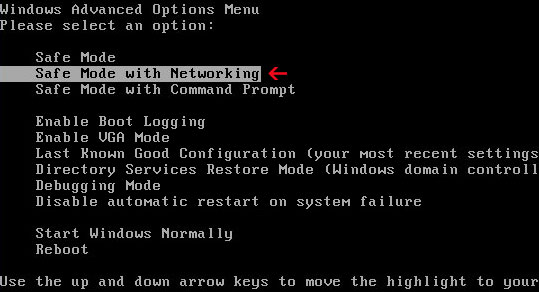

NOTE: Login as the same user you were previously logged in with in the normal Windows mode.


Manual System Security 2011 removal guide:

1. Right-click on System Security 2011 icon and select Properties. Then select Shortcut tab.

The location of the malware is in the Target box.

2. In our case the malicious file was located in C:\Windows\System32 folder. Select the malicious file, rename it and change a file name extension.

Original file: TcS22bF3nGaQWKf.exe


Renamed file: TcS22bF3nGaQWKf.vir


3. Restart your computer. After a reboot, download free anti-malware software from the list below and run a full system scan.

4. Download recommended anti-malware software (STOPzilla) and run a full system scan.

NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as Auto Infoistrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

5. Remove the TDSS/ZeroAccess rootkit (if exists). Please follow this removal guide: http://computertipsandguide.blogspot.com/2010/03/tdss-alureon-tidserv-tdl3-removal.html


Manual activation and System Security 2011 removal:

1. Choose to remove threats and manually activate the rogue program. Enter one of the following codes to activate System Security 2011.

9992665263
1148762586
1171249582
1186796371
1196121858
1225242171
1354156739
1579859198
1789847197

2. Download recommended anti-malware software (STOPzilla) and run a full system scan. This program will remove the virus from your computer.

NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as Auto Infoistrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. Remove the TDSS/ZeroAccess rootkit (if exists). Please follow this removal guide: http://computertipsandguide.blogspot.com/2010/03/tdss-alureon-tidserv-tdl3-removal.html


Associated System Security 2011 files and registry values:

Files:
  • C:\WINDOWS\system32\[SET OF RANDOM CHARACTERS].exe
  • C:\Documents and Settings\[UserName]\Application Data\csrss.exe
  • C:\Documents and Settings\[UserName]\Application Data\hTrkd58DeORldrQSystem Security 2011.ico
  • C:\Documents and Settings\[UserName]\Application Data\Microsoft\csrss.exe
  • C:\Documents and Settings\[UserName]\Desktop\System Security 2011.lnk
  • C:\Documents and Settings\[UserName]\Local Settings\Temp\[SET OF RANDOM CHARACTERS].tmp
  • C:\Documents and Settings\[UserName]\Start Menu\Programs\System Security 2011\System Security 2011.lnk
Registry values:
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS]"
Share this information with your friends: